

Check when the traffic increased
Compare the EDBB Traffic tab with application logs and scheduled jobs. Traffic includes incoming and outgoing data. Record when the increase began and whether the destination, protocol or service is expected.Measure live traffic
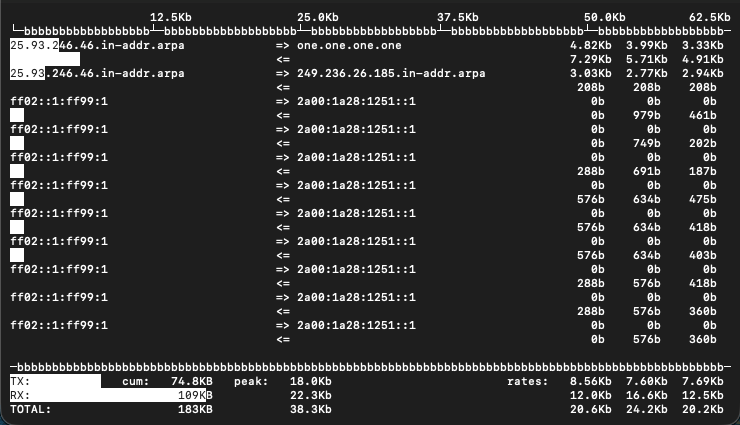
On Debian or Ubuntu, install the monitoring tools from your distribution’s repositories:eth0 below with your VPS’s network interface. Run iftop to see the connections using the most bandwidth:
q to exit. These are live measurements, not a reconstruction of traffic from before the tool was running.
Find the process using the traffic
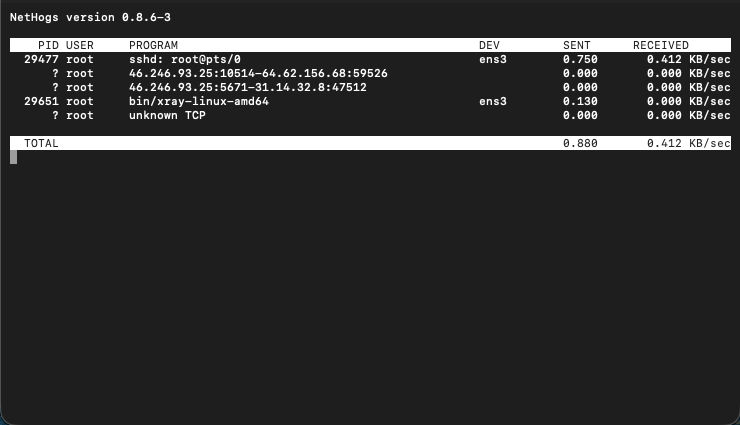
Runnethogs to group current traffic by process:
q to exit.
Preserve evidence before stopping a process
Record the process ID, command line, executable path, connections and relevant logs while the process exists. For example, replace1234 with the PID you found:
/proc/PID/ entries disappear when a process exits. Store evidence with restricted access on a separate system if an incident investigation requires it.
Do not run blanket removal commands for directories or executable names. Do not execute a suspicious file to identify it.
Stop unwanted activity
Use the VNC console as a recovery path before changing the firewall. Restrict the affected service or stop it after identifying it and preserving necessary evidence. Ordinary UFW rules filter traffic by network properties; they do not identify a malicious process by its name. For suspected compromise, rotate exposed credentials from a trusted device, investigate persistence and affected accounts, and consider rebuilding from a trusted image after preserving needed evidence and data. A deleted executable does not prove that the system is clean. If you received an abuse notice, follow responding to abuse and reply with your findings and remediation. See SSH hardening and backups.Keep a usage history
vnstat records interface totals after it is installed and running. Enable its service and check the interface:
sudo vnstat --add -i eth0, then restart the vnstat service. Allow time for it to collect data. Use vnstat -d -i eth0 for daily totals.
Local tools may use different units or time periods from the panel. EDBB traffic includes incoming plus outgoing data; use the Traffic tab to check the allowance and refill date. EDBB reads interface counters and does not identify which application generated the traffic for you.